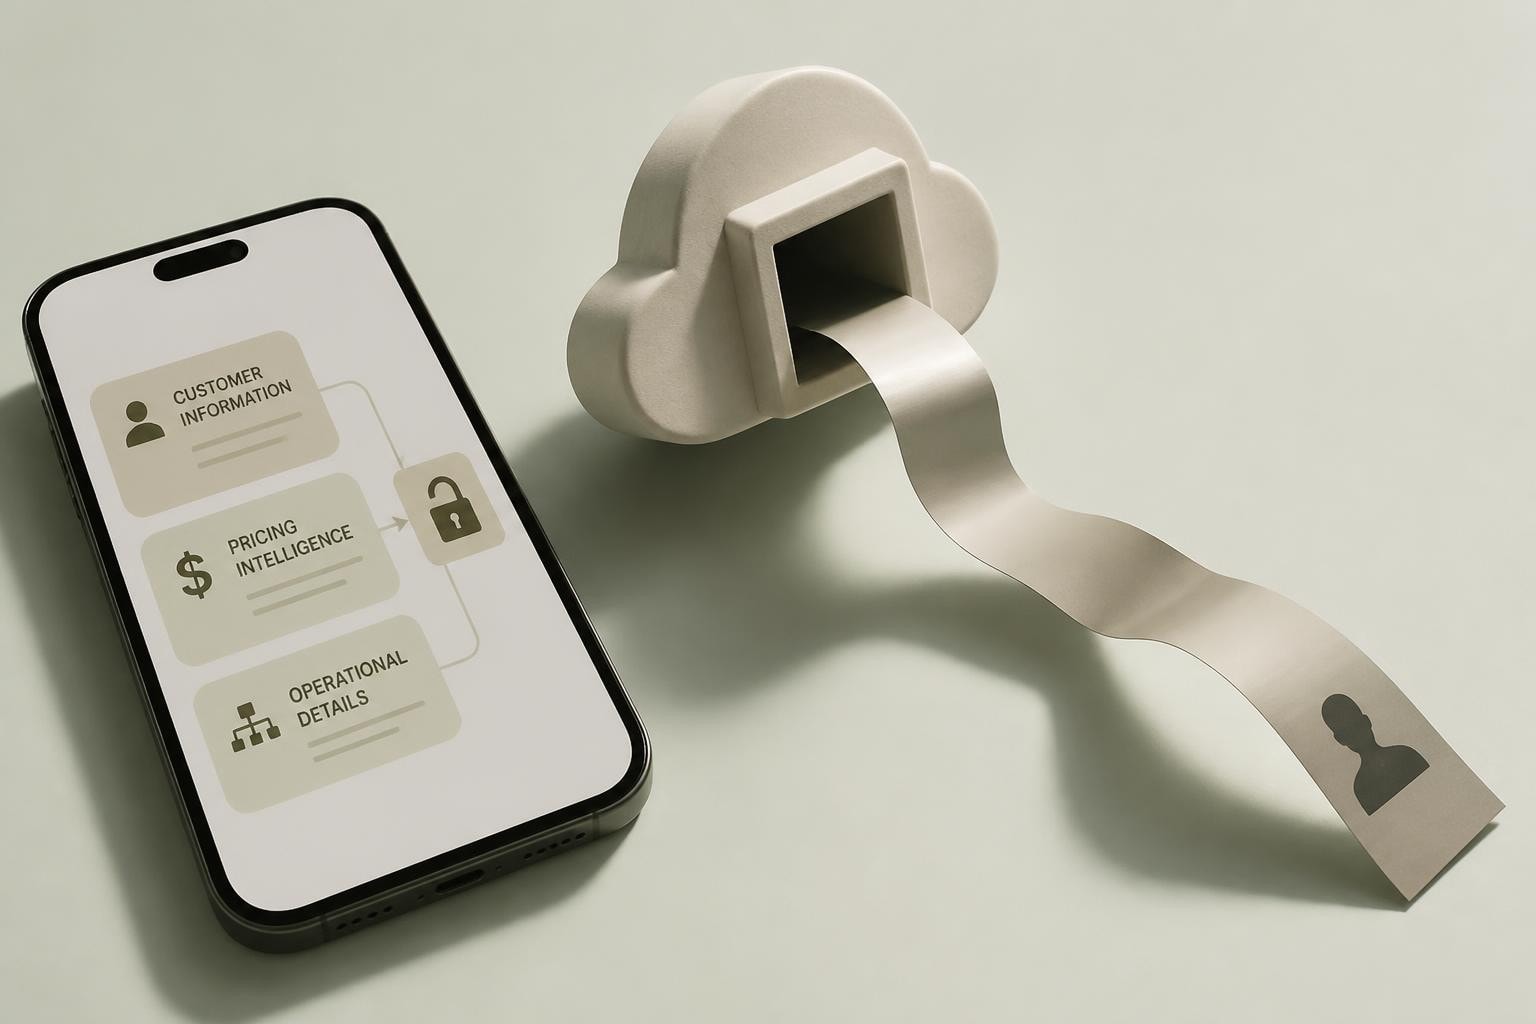
An AI leak represents one of the most insidious threats to modern business operations, silently draining revenue, exposing sensitive customer data, and eroding competitive advantage. Unlike traditional data breaches that involve external hackers breaking through firewalls, an AI leak occurs when artificial intelligence systems inadvertently expose training data, reveal proprietary business logic, or leak confidential information through their outputs. For local service businesses deploying AI to scale operations, understanding and preventing these leaks isn't just a technical concern-it's a fundamental revenue protection strategy that directly impacts customer retention, regulatory compliance, and market position.
What Constitutes an AI Leak in Business Operations
An AI leak manifests in multiple forms, each carrying distinct implications for revenue operations. The most common category involves training data exposure, where machine learning models unintentionally memorize and reproduce sensitive information from their training sets. This phenomenon becomes particularly dangerous when businesses feed customer records, pricing strategies, or operational details into AI systems without proper data hygiene protocols.
Membership Inference Attacks and Customer Privacy
Membership inference attacks represent a sophisticated form of AI leak where adversaries determine whether specific data points were included in a model's training set. Research from Columbia University demonstrates how attackers can query AI models to infer the presence of individual customer records, potentially exposing sensitive business relationships or transaction histories.
For local service businesses, this creates immediate revenue risks:
Customer trust erosion when clients discover their data was exposed
Competitive intelligence leakage revealing pricing strategies or service packages
Regulatory penalties under data protection frameworks
Reputational damage that directly impacts customer acquisition costs
The financial impact extends beyond immediate fines. When customers lose confidence in data handling practices, lifetime value contracts dissolve, referral rates plummet, and customer acquisition costs spike as negative reviews proliferate across digital channels.
Revenue Operations Vulnerabilities Created by AI Leaks
The intersection of AI leaks and revenue operations creates a perfect storm for local service businesses. Unlike enterprise corporations with dedicated security teams, smaller operations often deploy AI tools without fully understanding the data exposure risks embedded in their architecture.
Customer Journey Data Exposure
Every interaction in your customer journey-from initial contact through conversion, service delivery, and retention-generates data that feeds modern AI systems. When an AI leak occurs, this entire revenue pipeline becomes visible to competitors or malicious actors. They gain insights into your conversion rates, follow-up sequences, objection handling scripts, and reactivation strategies.
The AI Scaling Strategy Audit helps businesses identify where customer journey data intersects with AI systems, quantifying the exposure risk at each touchpoint. By mapping data flows through acquisition, conversion, and retention phases, service businesses can pinpoint exactly which revenue-generating processes face the highest AI leak vulnerability.
This systematic assessment reveals structural weaknesses before they transform into active leaks that compromise competitive positioning.
Operational Intelligence Leakage
Beyond customer data, AI systems often absorb operational intelligence that defines competitive advantage. Scheduling algorithms, resource allocation models, pricing optimization rules, and service delivery workflows all contain proprietary logic that drives profitability. When these elements leak through AI outputs, competitors can reverse-engineer your entire operational playbook.
For businesses leveraging AI for business operations, the challenge intensifies. The more sophisticated your automation becomes, the more valuable the intelligence embedded within those systems-and the greater the potential damage from an AI leak.
Regulatory and Compliance Dimensions of AI Leaks
The legal landscape surrounding AI leaks continues evolving rapidly, creating compliance obligations that directly impact revenue operations. Regulatory bodies now treat AI data exposure with the same severity as traditional data breaches, imposing substantial penalties that can devastate local service businesses operating on tight margins.
Federal Trade Commission Enforcement Actions
The FTC's 2023 privacy and data security update demonstrates increasing scrutiny of AI systems that mishandle consumer data. Enforcement actions now target companies whose AI tools inadvertently expose personal information, treating these incidents as unfair or deceptive practices under Section 5 of the FTC Act.
For revenue operations, this translates to:
Direct financial penalties that immediately impact profit margins
Mandatory operational changes requiring expensive system overhauls
Consumer notification requirements that damage brand reputation
Ongoing monitoring obligations that increase operational overhead
A single AI leak incident can trigger a cascade of compliance costs that exceed the original technology investment by orders of magnitude.
European AI Act Transparency Obligations
The European Commission's AI transparency guidelines establish explicit disclosure requirements for businesses deploying AI systems. Even local service companies with primarily domestic operations face these obligations when serving any EU residents or processing data that might fall under GDPR jurisdiction.
These transparency requirements demand clear documentation of:
What data feeds into AI systems
How models process and store information
What safeguards prevent unintended data exposure
How the business responds to potential AI leaks
What rights customers have regarding their AI-processed data
Non-compliance creates both direct regulatory risk and indirect revenue damage as customers increasingly prioritize data protection when selecting service providers.
Technical Defenses Against AI Leak Vulnerabilities
Protecting revenue operations from AI leaks requires a multi-layered technical approach that balances security with operational efficiency. Local service businesses cannot afford to deploy enterprise-grade security infrastructure, but they can implement focused defenses that address the highest-risk leak vectors.
Input Validation and Context Hygiene
Microsoft's engineering guidance on input and retrieval hygiene provides practical controls for preventing prompt injection and retrieval poisoning attacks. These defenses create barriers between user inputs and sensitive system contexts, ensuring that malicious prompts cannot trick AI systems into leaking protected information.
Key implementation steps include:
Sanitizing all external inputs before they reach AI processing layers
Segregating customer data from publicly accessible model contexts
Implementing output filtering to catch inadvertent data exposure
Monitoring API interactions for suspicious extraction patterns
Maintaining audit trails that document every data access request
For businesses building business automation systems, these controls integrate naturally into the development workflow when addressed from the outset rather than retrofitted after deployment.
Revenue Recovery Strategies After AI Leak Incidents
Despite robust defenses, AI leak incidents may still occur. The speed and effectiveness of your response directly determines whether the incident becomes a minor setback or a revenue catastrophe. Local service businesses must prepare incident response protocols before leaks occur, not during crisis management.
Immediate Containment and Assessment
The first 24 hours after discovering an AI leak prove critical for revenue preservation. Immediate actions should focus on stopping ongoing exposure, assessing the scope of compromised data, and quantifying the potential revenue impact across your customer base.
Containment priorities:
Disable affected AI systems or endpoints
Preserve logs and evidence for forensic analysis
Identify exactly which data elements were exposed
Determine which customers or transactions were affected
Assess whether competitors accessed leaked information
This rapid assessment enables targeted customer communication rather than panic-driven mass notifications that amplify reputational damage beyond the actual incident scope.
Customer Communication and Trust Restoration
How you communicate an AI leak to affected customers fundamentally shapes whether they remain loyal or defect to competitors. Transparency builds trust, but poorly executed disclosure destroys it. The message must acknowledge the incident, explain what happened in accessible terms, detail protective measures taken, and demonstrate genuine commitment to preventing recurrence.
Effective revenue automation strategy includes pre-built incident communication templates that can be rapidly customized and deployed. These templates ensure consistent messaging across email, SMS, and direct outreach channels while maintaining the personal touch that local service relationships require.
Regulatory Notification and Compliance
Beyond customer communication, most jurisdictions require formal breach notifications to regulatory authorities when AI leaks expose personal information. Timing requirements vary, but typically mandate notification within 72 hours of discovery. Failure to meet these deadlines compounds the revenue damage with additional penalties and enforcement actions.
Working with legal counsel to prepare notification templates in advance reduces response time and ensures compliance even under crisis conditions. These templates should address the specific requirements of relevant frameworks while maintaining clarity for non-technical regulators.
Preventing AI Leaks in AI Revenue Operations Systems
For businesses deploying AI specifically to optimize revenue operations, leak prevention becomes inseparable from system design. Every component that touches customer data, pricing logic, or operational intelligence requires security controls matched to the sensitivity of that information.
Data Minimization in Training Sets
The most effective defense against AI leaks is ensuring sensitive information never enters training data in the first place. Data minimization principles dictate that AI systems should receive only the minimum information necessary to perform their intended function.
Before feeding customer records into AI models, businesses should:
Remove personally identifiable information that isn't essential for model performance
Aggregate data at appropriate levels to obscure individual transactions
Tokenize sensitive fields like contact information or payment details
Implement retention limits that automatically purge old training data
Document data lineage to understand exactly what information exists where
This approach reduces exposure risk while maintaining the predictive power that makes AI valuable for revenue optimization. Properly anonymized data still reveals patterns in customer behavior, service demand, and conversion dynamics without creating leak vulnerabilities.
Zero-Trust Architecture for AI Systems
Zero-trust principles assume that any component might be compromised, requiring verification at every interaction point. Applied to AI systems, this means treating model outputs as potentially malicious and validating them before they reach customers or business users.
Implementing zero-trust for AI involves:
Authenticating every API request regardless of apparent source
Limiting model access to specific functions rather than broad permissions
Encrypting data in transit and at rest throughout the AI pipeline
Segmenting networks to isolate AI systems from other infrastructure
Monitoring continuously for anomalous access patterns or output behaviors
These controls create defense in depth, ensuring that even if one layer fails, additional safeguards prevent complete system compromise and revenue data exposure.
Measuring the Financial Impact of AI Leak Prevention
Security investments compete with revenue-generating initiatives for limited budgets. Local service businesses need clear frameworks for quantifying the return on AI leak prevention, demonstrating that these measures protect existing revenue rather than merely representing cost centers.
Revenue at Risk Calculation
Begin by inventorying all customer data, pricing intelligence, and operational secrets that flow through AI systems. For each category, estimate the revenue impact if competitors gained access or if regulatory penalties materialized.
Sample calculation framework:
Data Category | Revenue Exposure | Probability of Leak | Expected Annual Loss |
|---|---|---|---|
Customer Contact Lists | $150,000 | 15% | $22,500 |
Pricing Algorithms | $300,000 | 8% | $24,000 |
Conversion Scripts | $200,000 | 12% | $24,000 |
Service Delivery Workflows | $180,000 | 10% | $18,000 |
Total Expected Loss | $88,500 |
This quantification demonstrates that even modest security investments generate positive ROI when they reduce expected losses below implementation costs.
Customer Lifetime Value Protection
Beyond immediate revenue exposure, AI leaks damage customer lifetime value through trust erosion. Customers who experience data exposure incidents exhibit measurably lower retention rates, reduced expansion revenue, and decreased referral activity.
Measuring these impacts requires tracking cohorts affected by security incidents against control groups, revealing the true lifetime revenue impact that extends years beyond the initial leak. For subscription-based service businesses, a single major AI leak can suppress revenue growth for multiple quarters as damaged customer relationships slowly recover or churn entirely.
Building AI Leak Awareness Into Organizational Culture
Technical defenses only succeed when supported by organizational culture that prioritizes data protection at every level. Local service businesses often struggle with this cultural dimension because frontline staff may not understand how their daily actions influence AI leak risk.
Training Programs for Non-Technical Staff
Every employee who interacts with AI systems or handles customer data requires baseline training on AI leak risks and prevention protocols. This training should use concrete examples relevant to their specific roles rather than abstract security concepts.
Effective training modules address:
How AI systems learn from data and why that creates exposure risk
What information should never be entered into AI tools
How to recognize potential prompt injection attempts
When to escalate unusual AI behavior to technical staff
Why data protection directly impacts job security through revenue preservation
Regular refresher training ensures these principles remain top of mind as AI capabilities expand and new leak vectors emerge.
Incident Response Drills
Theoretical knowledge proves insufficient during actual crisis scenarios. Regular incident response drills simulate AI leak events, allowing teams to practice containment, assessment, communication, and recovery procedures under realistic pressure.
These exercises reveal gaps in protocols, communication breakdowns, and unclear ownership that would multiply damage during actual incidents. They also build organizational muscle memory, enabling faster, more effective responses when real leaks occur.
AI leak prevention directly determines whether your revenue operations deliver sustainable growth or gradually erode through unnoticed data exposure and competitive intelligence leakage. The technical, regulatory, and operational dimensions of this challenge require integrated solutions that protect sensitive information while preserving the efficiency gains that make AI valuable. Leverage Scaling helps local service businesses identify where AI systems create revenue exposure risks, quantify their financial impact, and implement protective measures that secure growth without sacrificing operational efficiency. Discover how Leverage OS systematically prevents the revenue leaks that undermine your competitive position and customer trust.